Prerequisites
- An AWS account, and permission to create IAM policies and roles in it.
- Your 12-digit AWS account ID, and the region your log groups are in.
- The external ID shown on the NOFire AI dashboard when you add the connection.
Step 1: Create IAM role
Open the AWS Management Console with an account that has permission to create IAM roles. Then follow the steps below:
- Access IAM: Navigate to the IAM service in the AWS console.
-
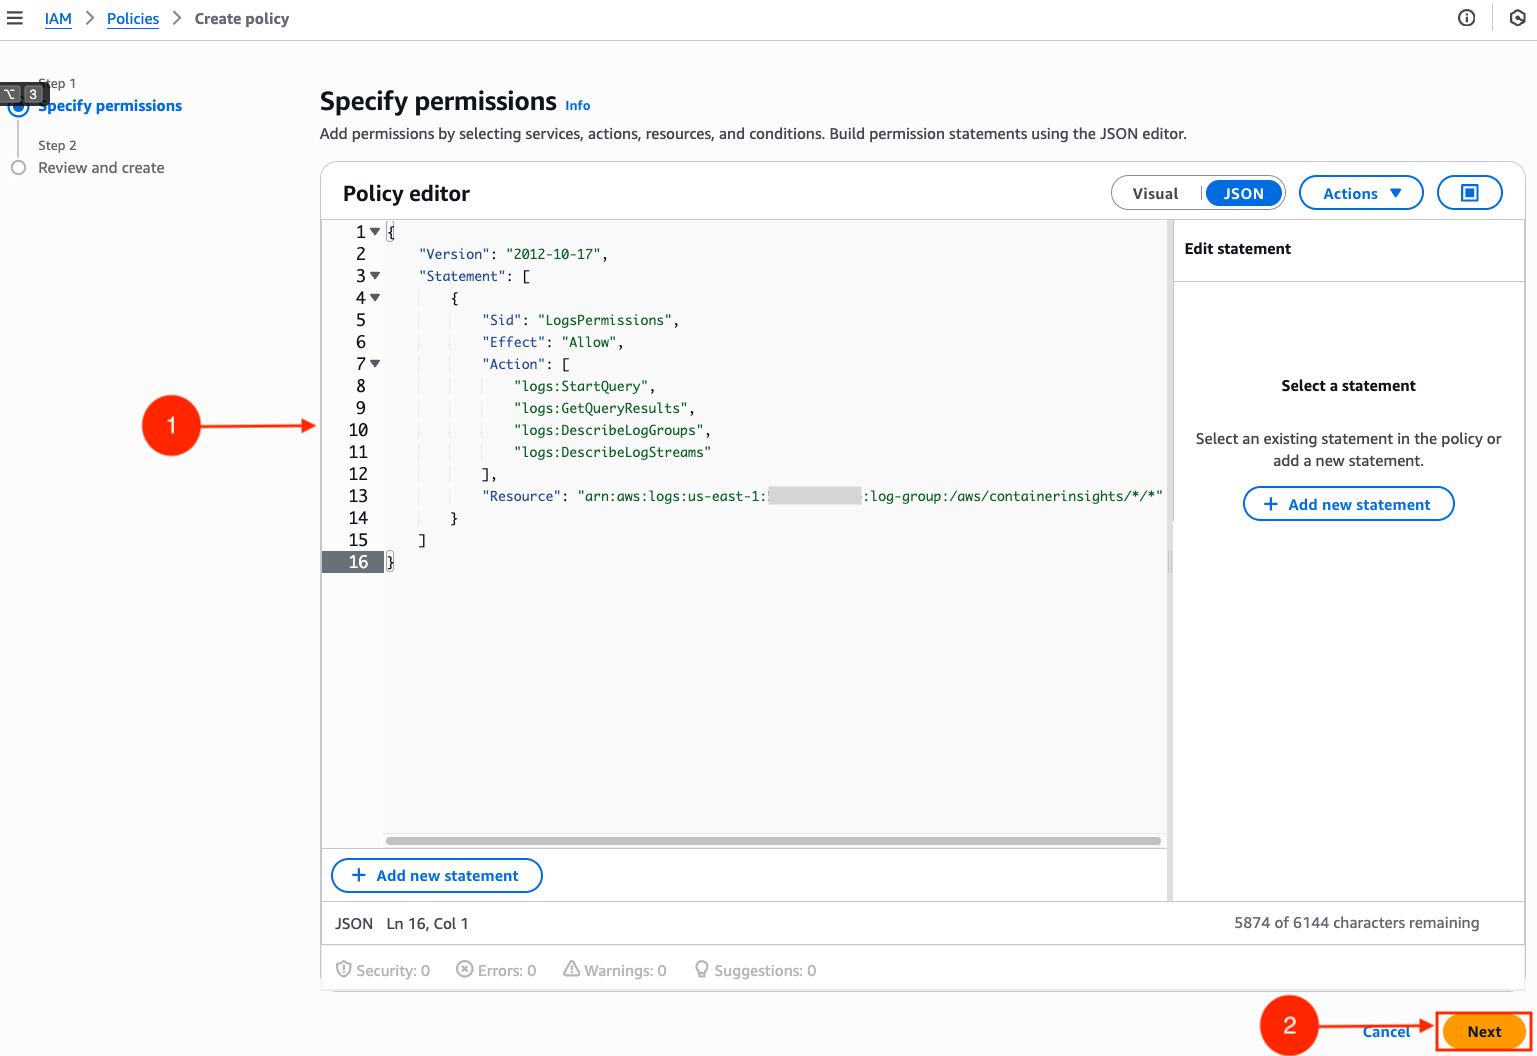
Copy the following IAM policy. You will attach it to the role that you create later.
nofireai-iam-policy.json
-
Create a new policy: In the navigation pane on the left, choose Policies > Create policy.
-
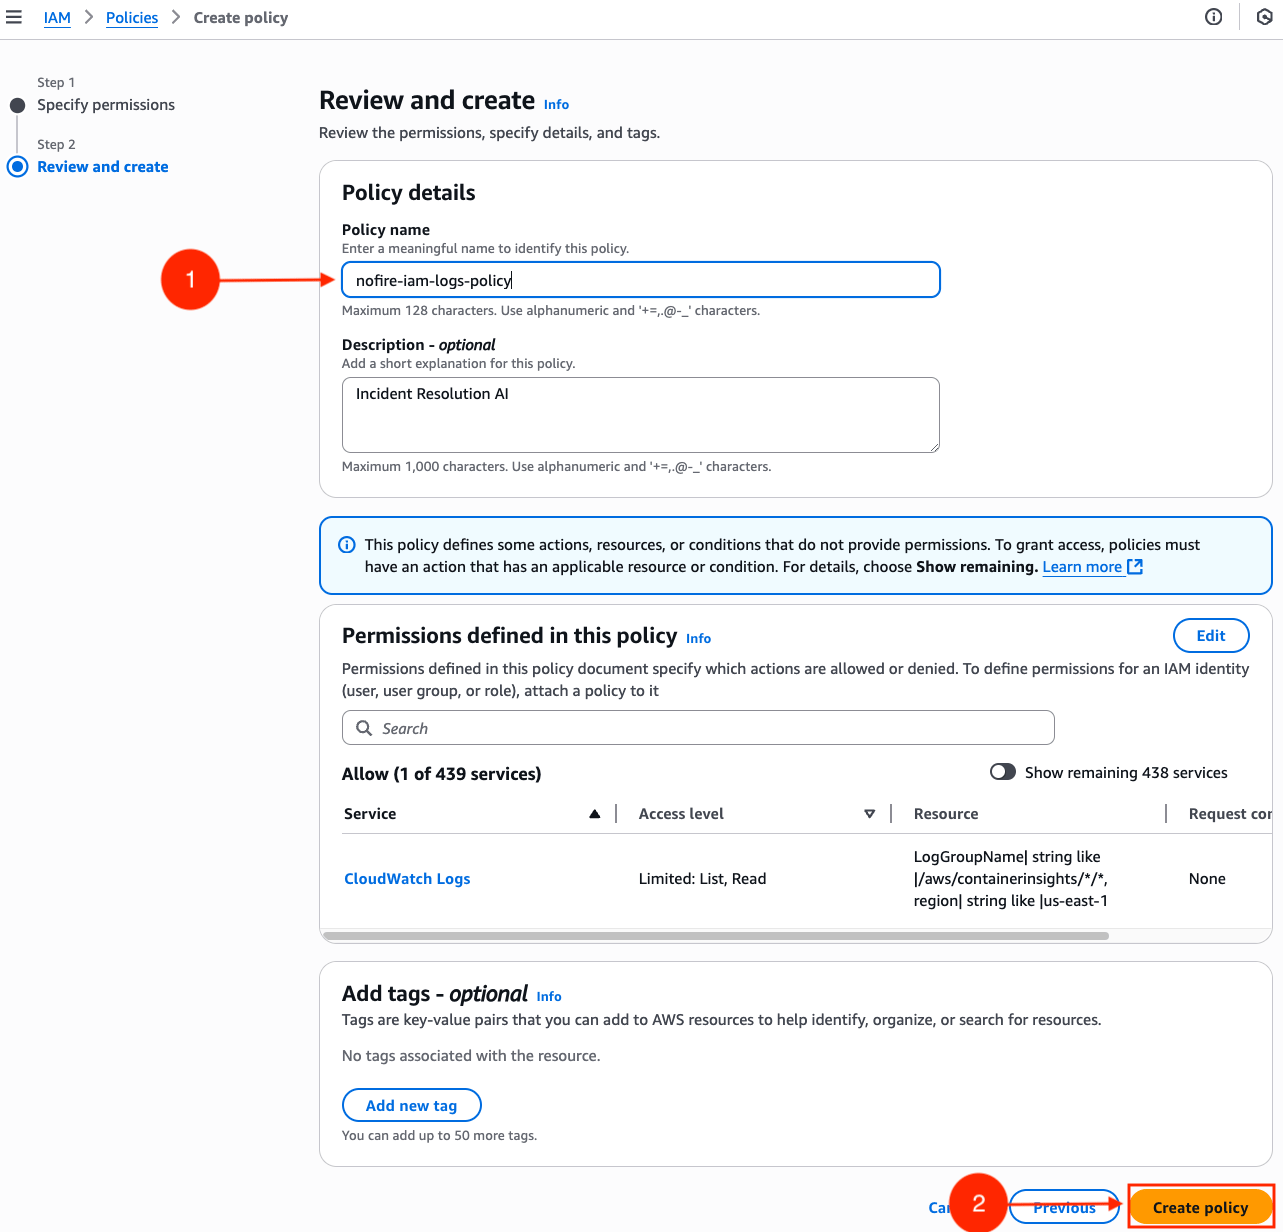
Finalize and review: Create a name and description for the IAM policy:
-
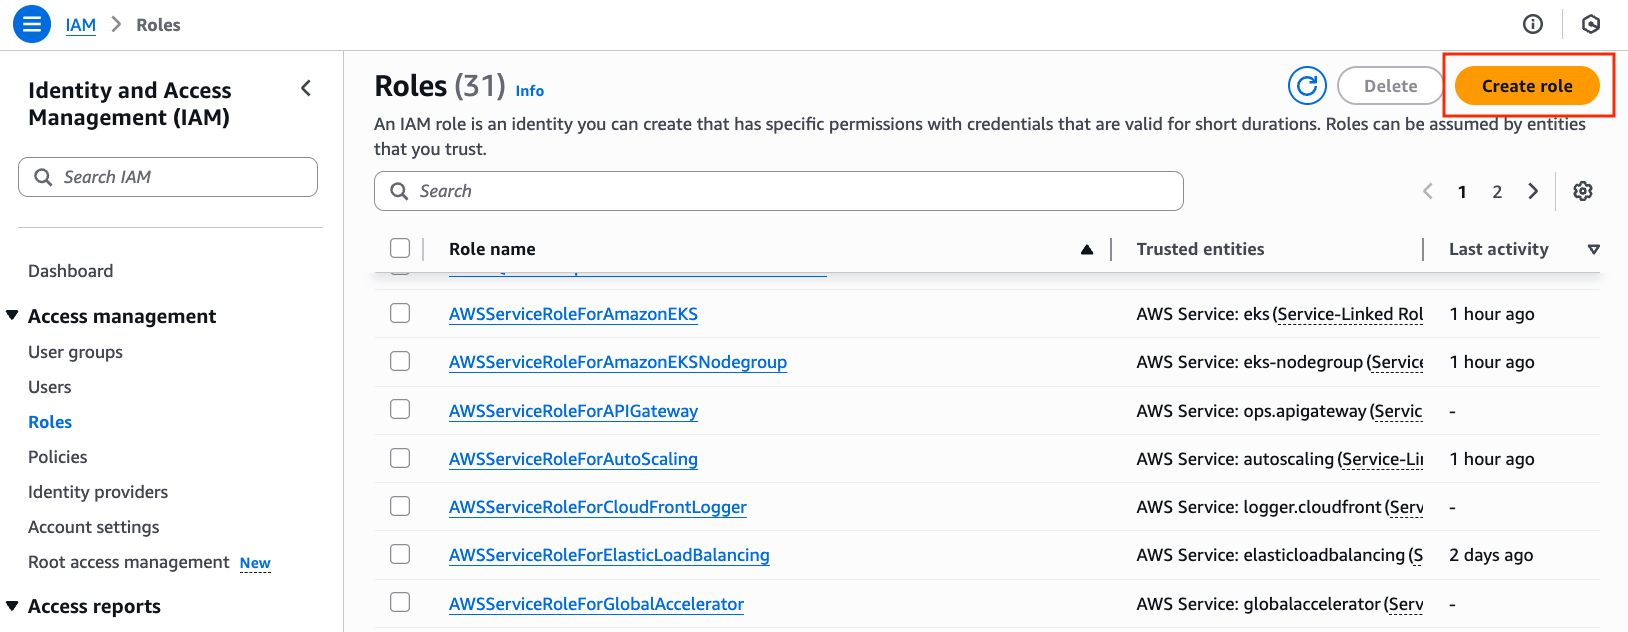
Create a new role: In the navigation pane on the left, choose Roles > Create role.
-
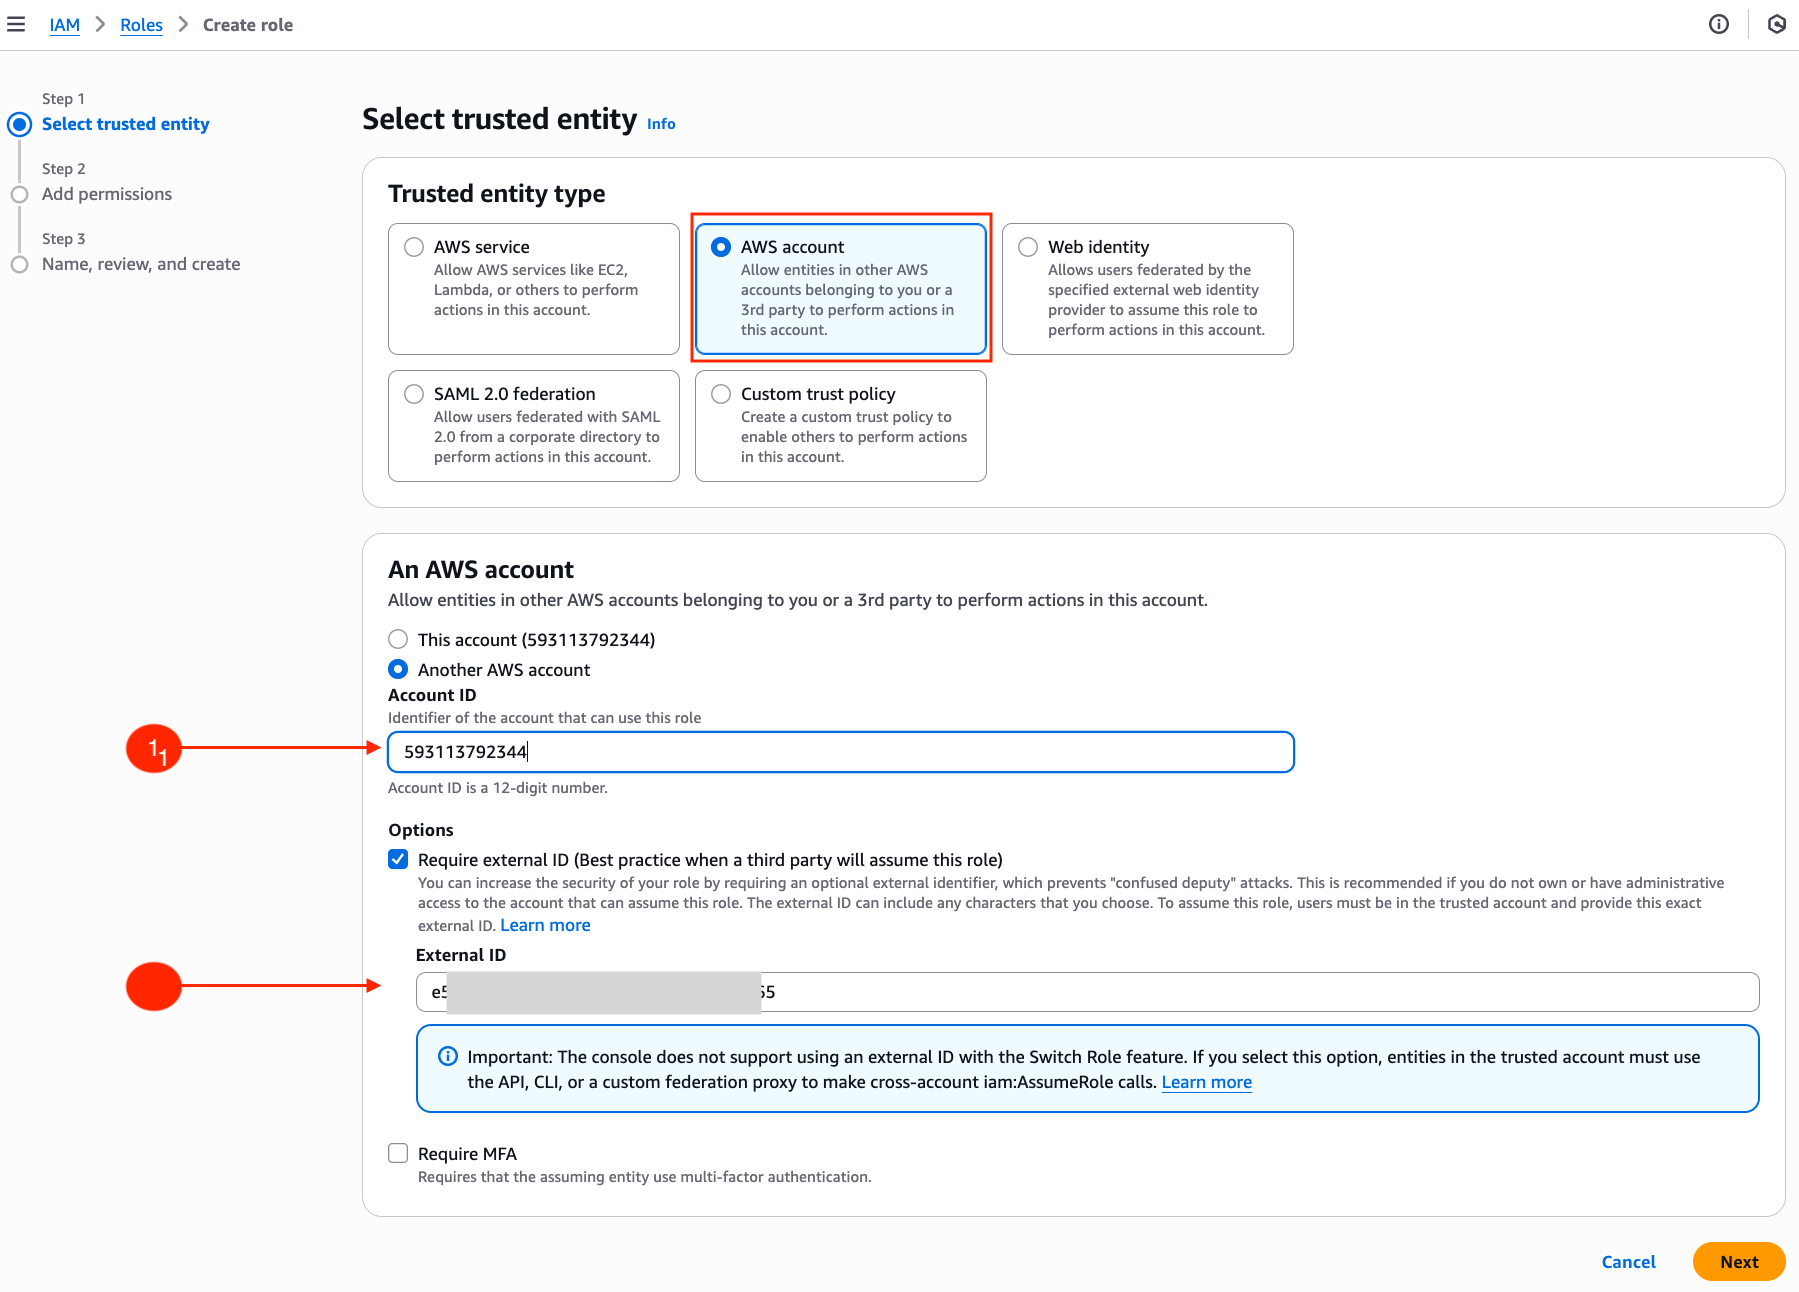
Enter credentials:
- Add NOFire AI’s Account ID: In the Account ID input box, paste the NOFire AI AWS Account ID: 593113792344. This gives NOFire AI access to the IAM role.
-
Add an External ID: Under Options, enter an external ID.
-
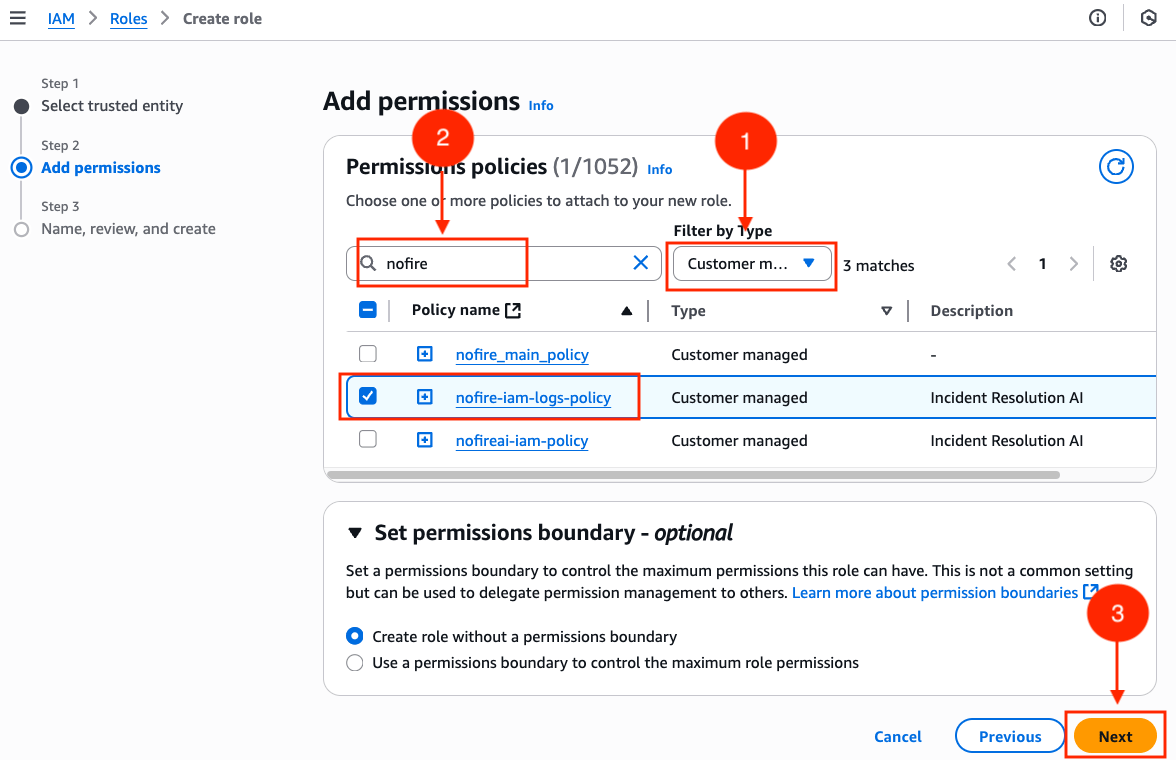
Assign permissions: On the permissions console, use the Filter and select Customer Managed. Search for the policy name that you provided in step 4, then click Next.
-
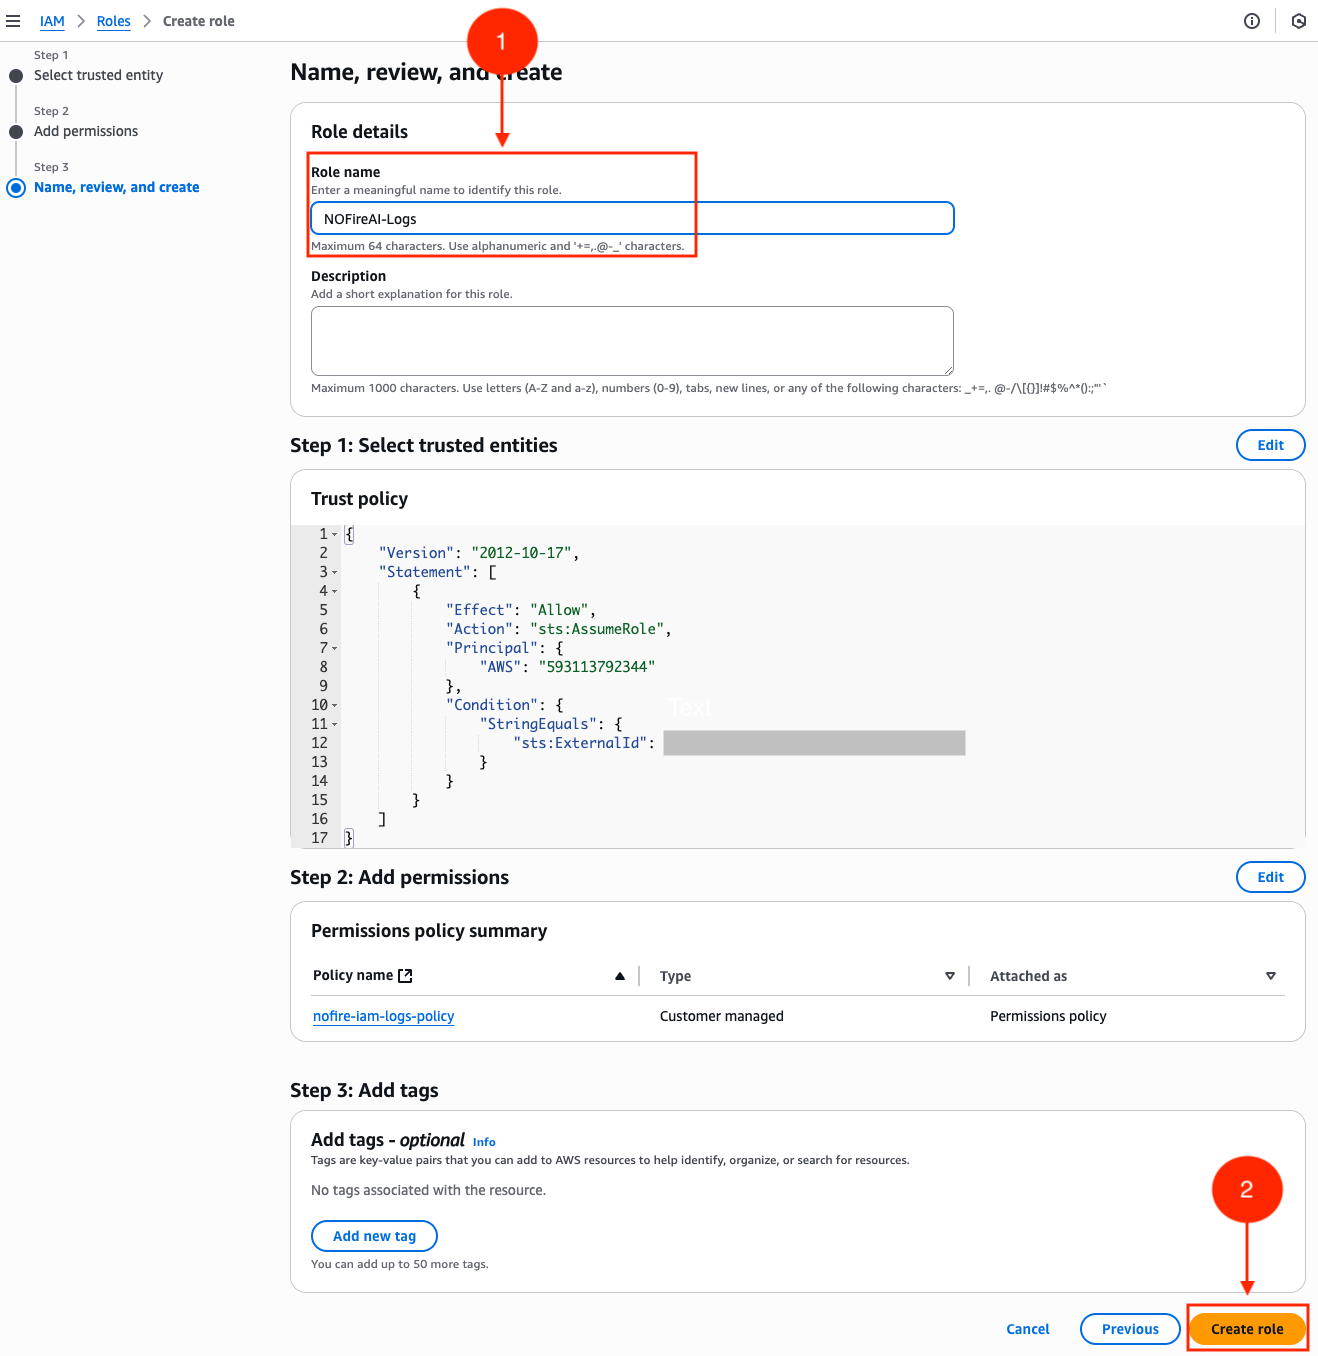
Finalize and review: Create a name and description for the IAM role, and then review the configurations.
-
If everything is correct, click the Create role button at the bottom right corner.
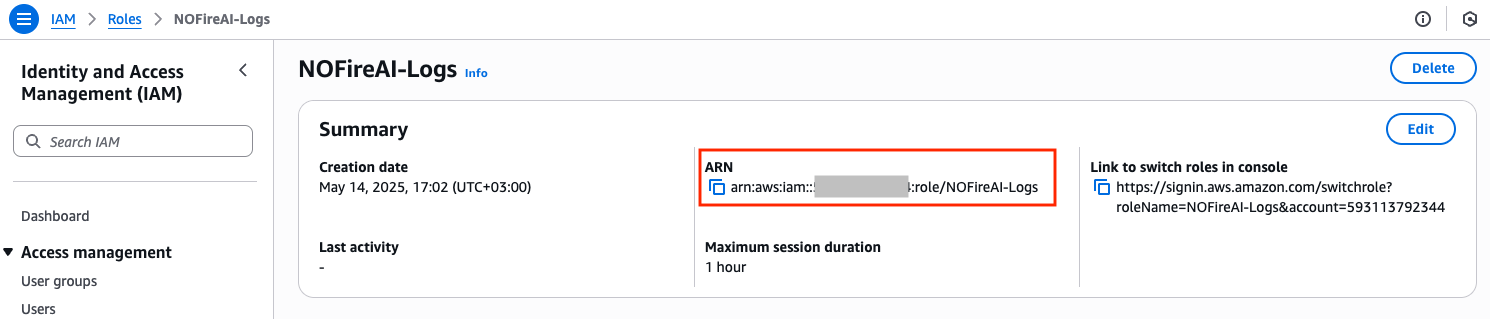
- Copy the Role ARN: After you create the role, open it and copy the role ARN. You will need this to complete the connection setup on the NOFire AI dashboard.
Step 2: Add AWS CloudWatch connection to NOFire AI
-
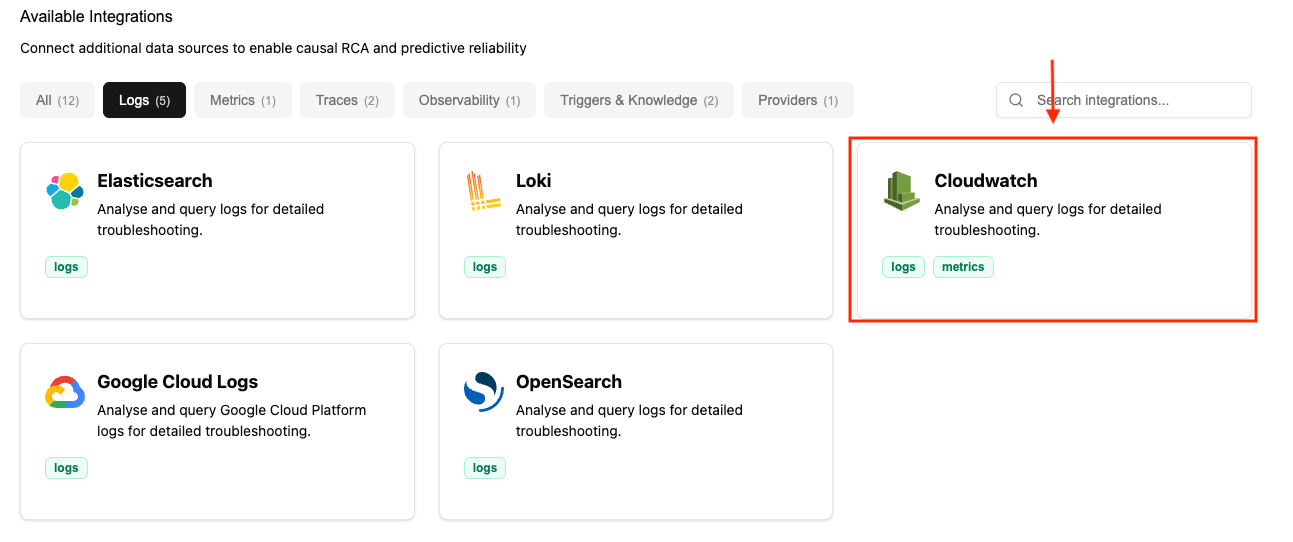
Go to Connections and click Connect on Cloudwatch.
-
Enter credentials:
- Name (for example, production)
- Region (for example, us-east-1)
- IAM Role ARN
-
External ID
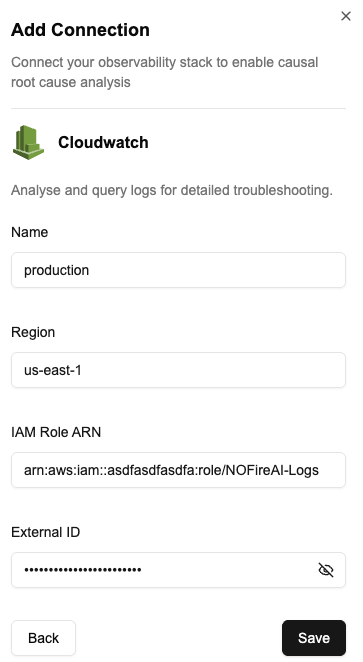
Click Save to create the connection
- After you connect to your log source, NOFire AI queries and analyzes logs on demand as part of its automated root cause analysis. Logs enrich the investigation process.
Test the connection
- Open the Connections dashboard and make sure that the CloudWatch connection status is READY. A connection that stays in an error state did not authenticate.
- Ask NOFire a question that needs logs, for example “show me the errors for the checkout service in the last hour”. An answer that quotes your log lines confirms the connection works end to end.
Troubleshooting
Connection test fails with an access-denied error
Connection test fails with an access-denied error
The external ID on the connection must match the one in the trust policy of the role exactly, and the trust policy must name the NOFire AI account ID
593113792344.The connection saves but returns no logs
The connection saves but returns no logs
The
Resource line in the policy names a region or an account ID that does not hold your log groups. Edit the policy and correct both values.