If you are running a self-hosted Loki instance, NOFire AI can connect securely using an AWS VPC PrivateLink. This ensures all traffic remains within your network boundary, following AWS security best practices.
Prerequisites
- A Loki instance that NOFire AI can reach.
- The query endpoint URL of that instance.
Step 1: Setup Loki instance integration
Grafana Cloud (skip for on-prem)
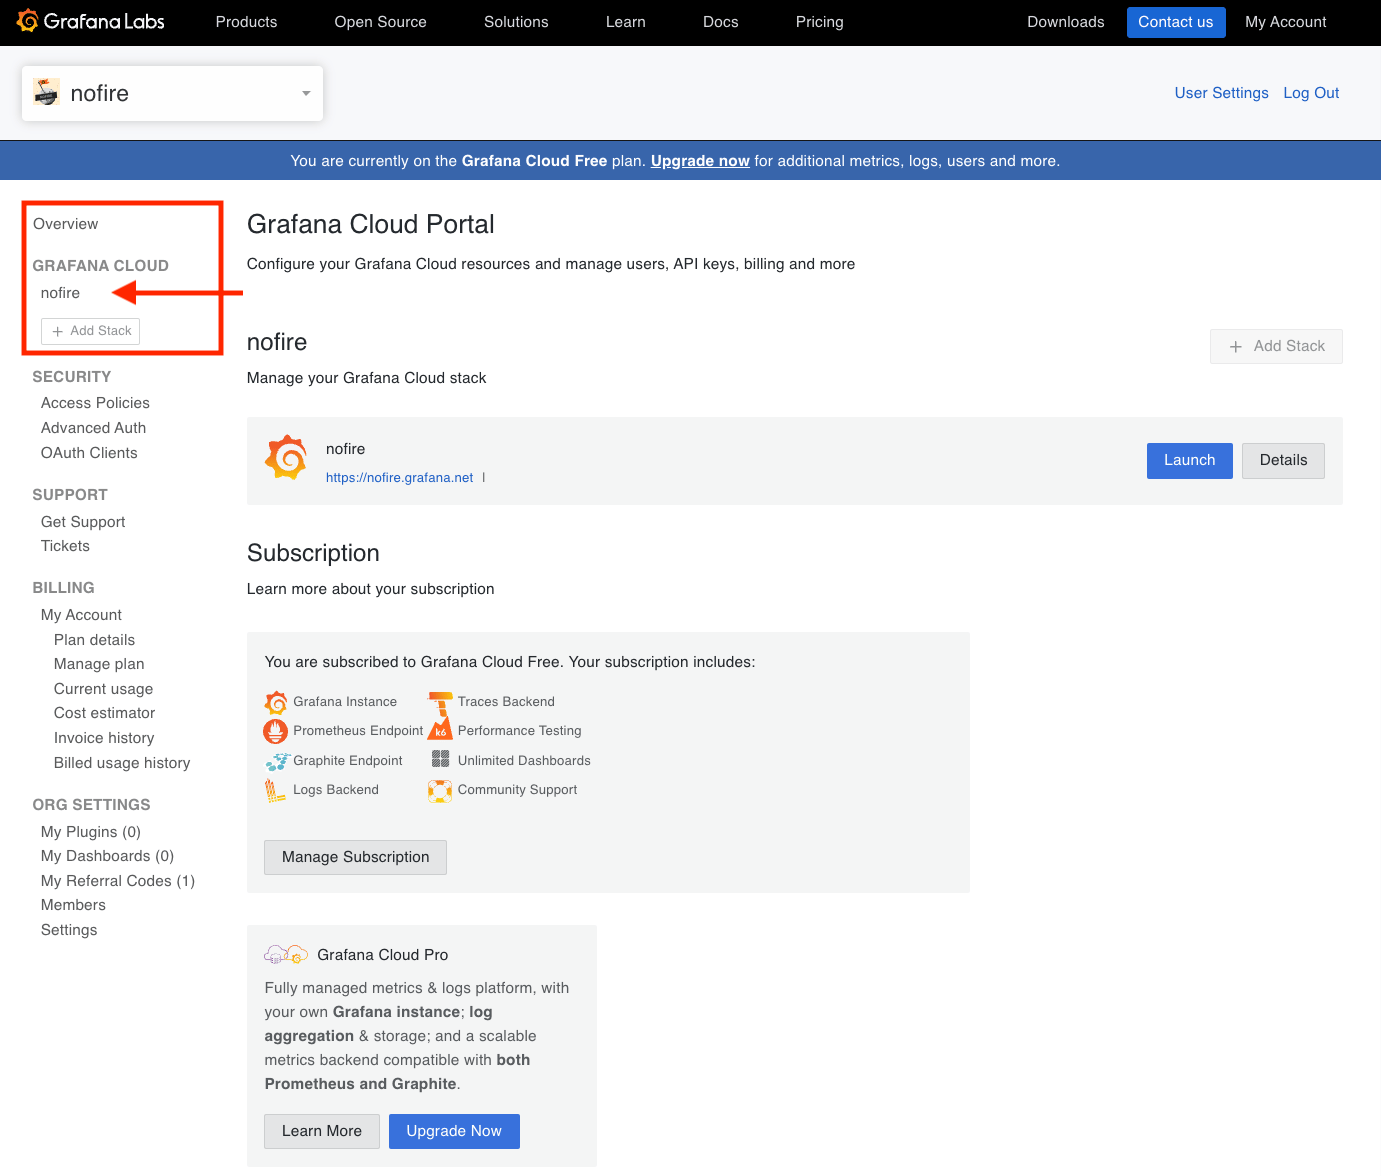
- Sign-in to portal https://grafana.com/auth/sign-in
- Select your Grafana stack eg. nofire.\
- Select Loki details.\
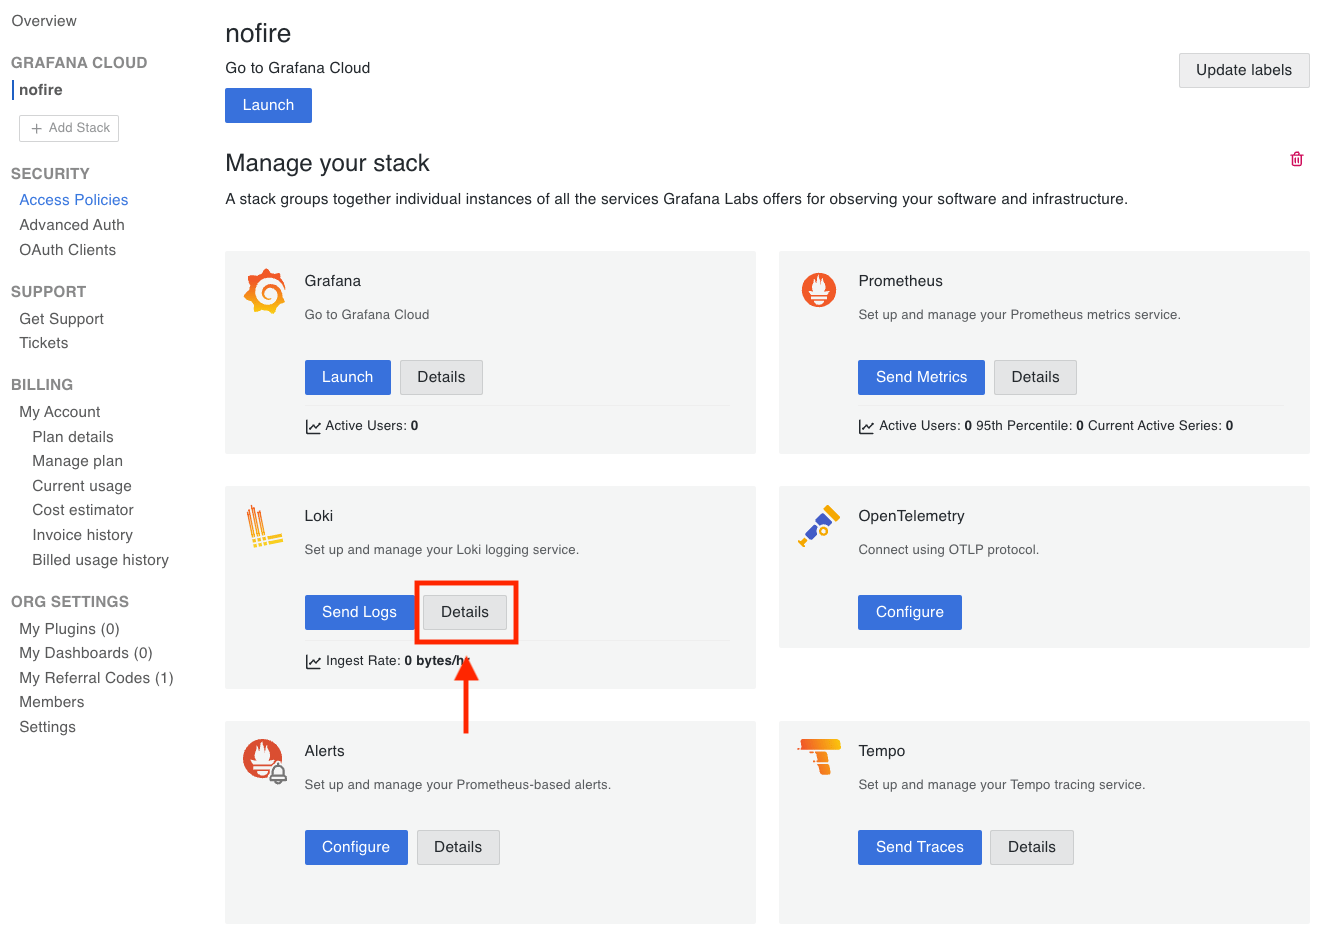
- Copy to clipboard: The Query Endpoint and keep it in a note.\

- Copy to clipboard: The User and keep it in a note.\
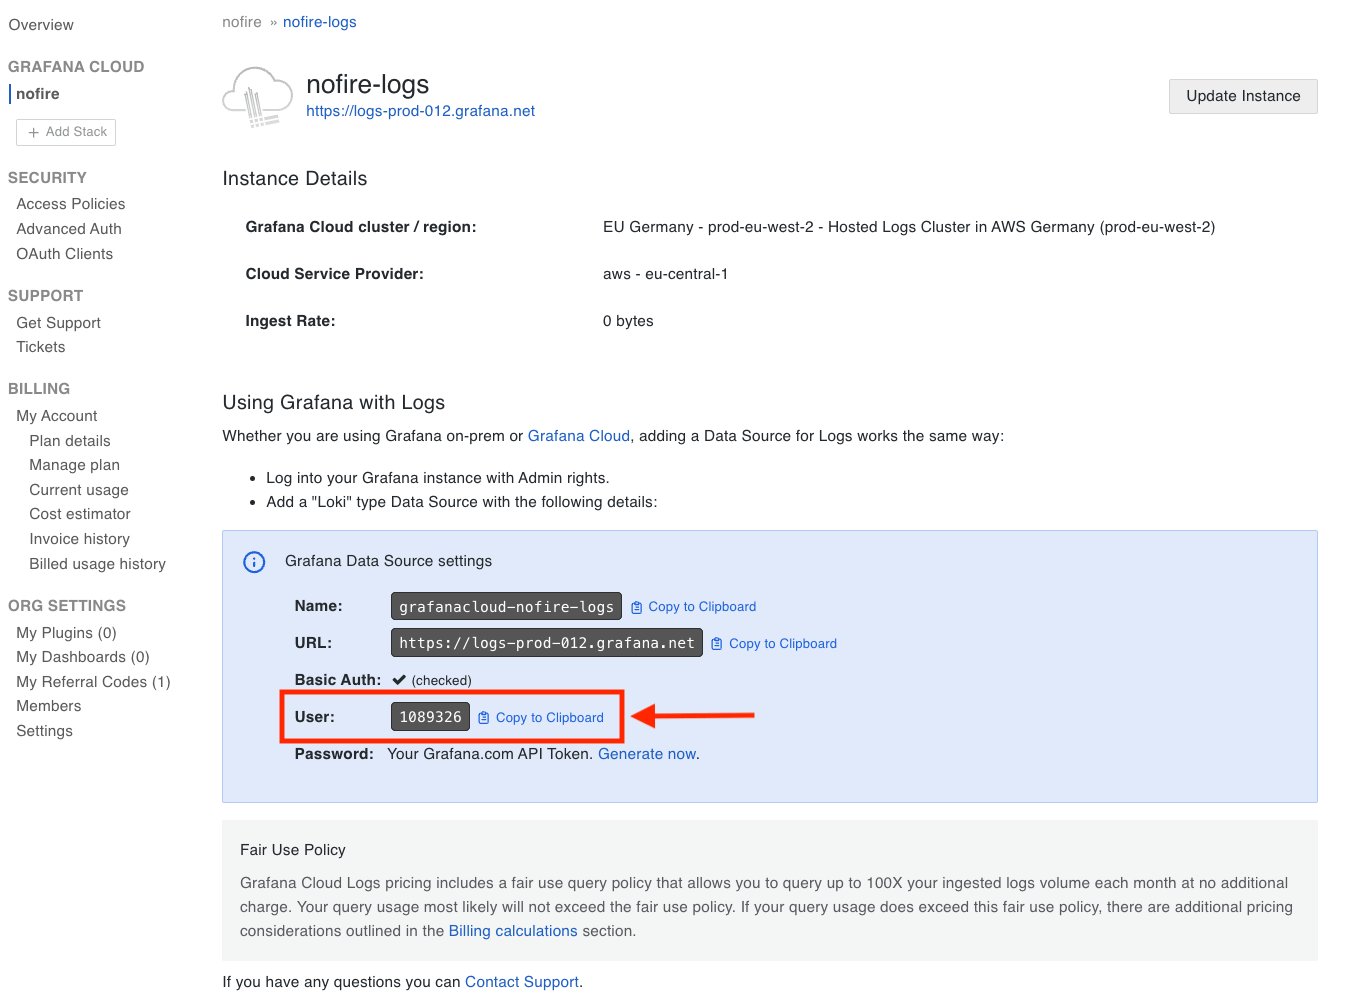
- Create Cloud Access Policy: For your stack with
logs:readscope only\
- Add a token to this newly create access policy\

- Set a name and an expiration date: based on your preference and generate the token.\

Step 2: Add Loki connection to NOFire AI
-
Go to Connections and click Connect on Loki.
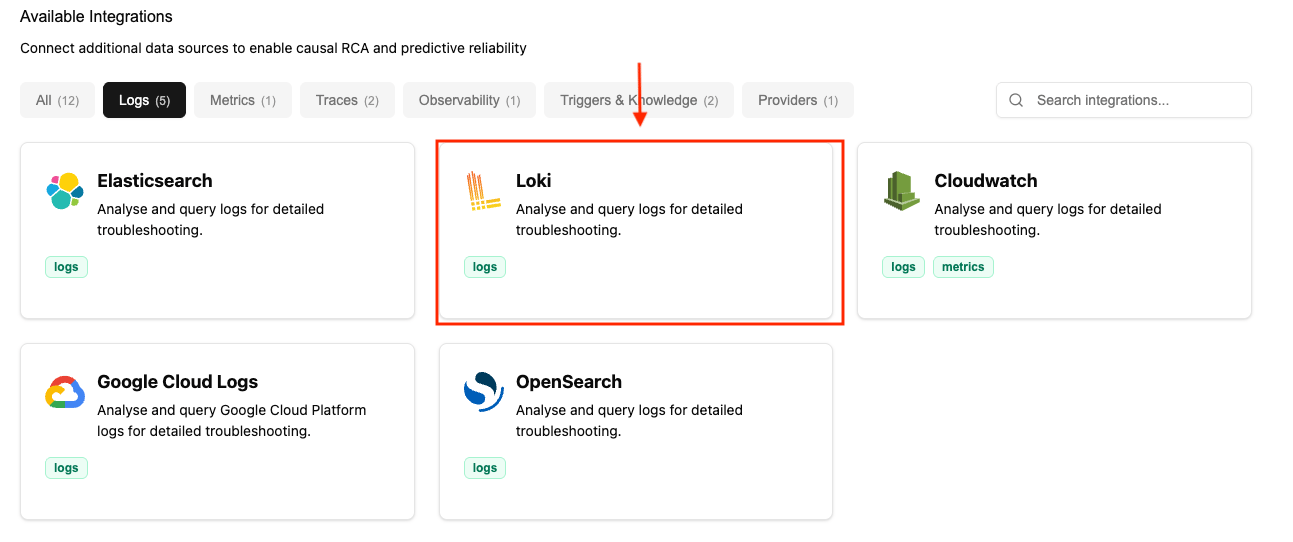
-
Enter Name (for example, production), the Loki URL, and Username/Password (optionally for on-prem, required for Grafana Cloud):
Once the connection to your log source is established, NOFire AI will query and analyze logs on-demand as part of its automated root cause analysis. Logs are used to enrich the investigation process.
Test the connection
- Open the Connections dashboard and make sure that the Loki connection status is READY. A connection that stays in an error state did not authenticate.
- Ask NOFire a question that needs logs, for example “show me the errors for the checkout service in the last hour”. An answer that quotes your log lines confirms the connection works end to end.
Troubleshooting
The connection saves but returns no logs
The connection saves but returns no logs
The URL points at a different stack, or the labels you query do not exist in that Loki instance. Run the same query in Grafana against the same URL.